ZENTARA
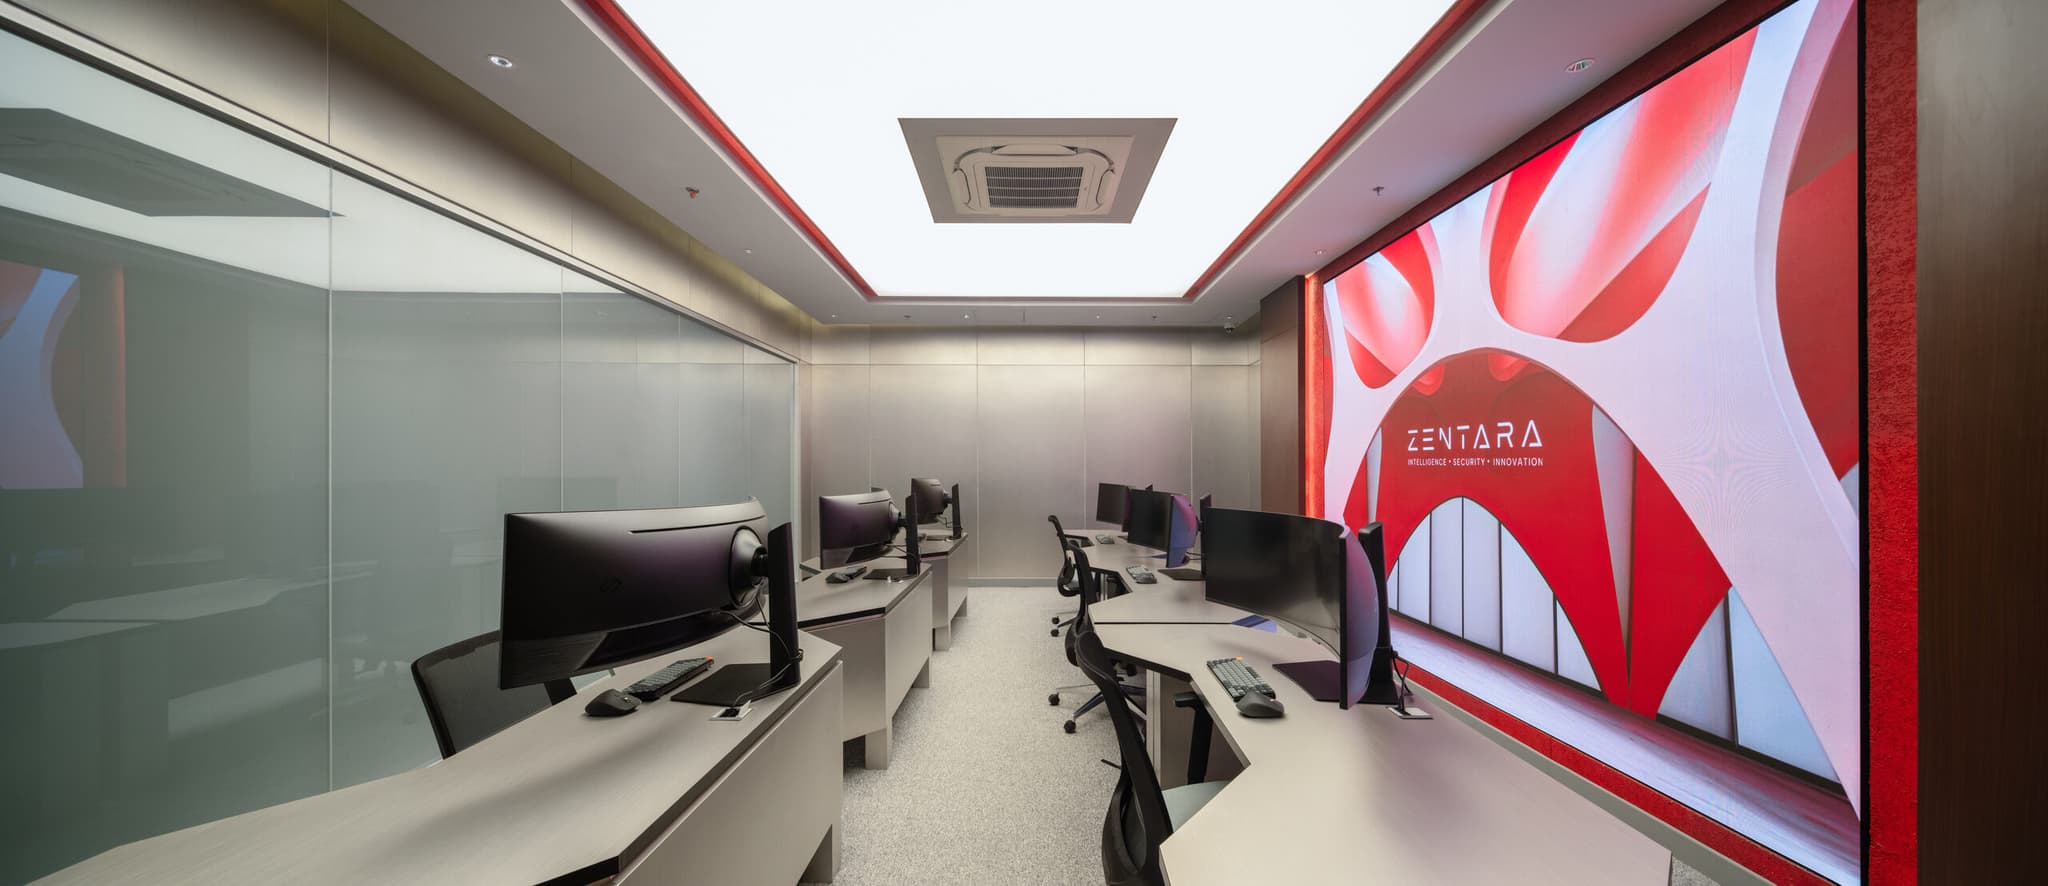
The Zentara SOC — the 24/7 watch room in Greater Jakarta

Security Operations · Flagship service

Managed SOC.

Your security. Your infrastructure. Our expertise.

  • 15 min

    P1 response SLA

  • 2 hrs

    P1 containment SLA

  • 24/7

    Certified analyst coverage

Get a free SOC assessment

Tell us about your environment. We'll recommend the right SOC model and the next steps.

I agree to Zentara storing and processing my details in order to respond to this enquiry.

Certified & audited operations

BSSN — Badan Siber dan Sandi NegaraISO/IEC 27001 CertifiedISO/IEC 42001:2023 CertifiedAICPA SOC 2 Type 2
Verify at our trust centre

The landscape

What companies are facing right now

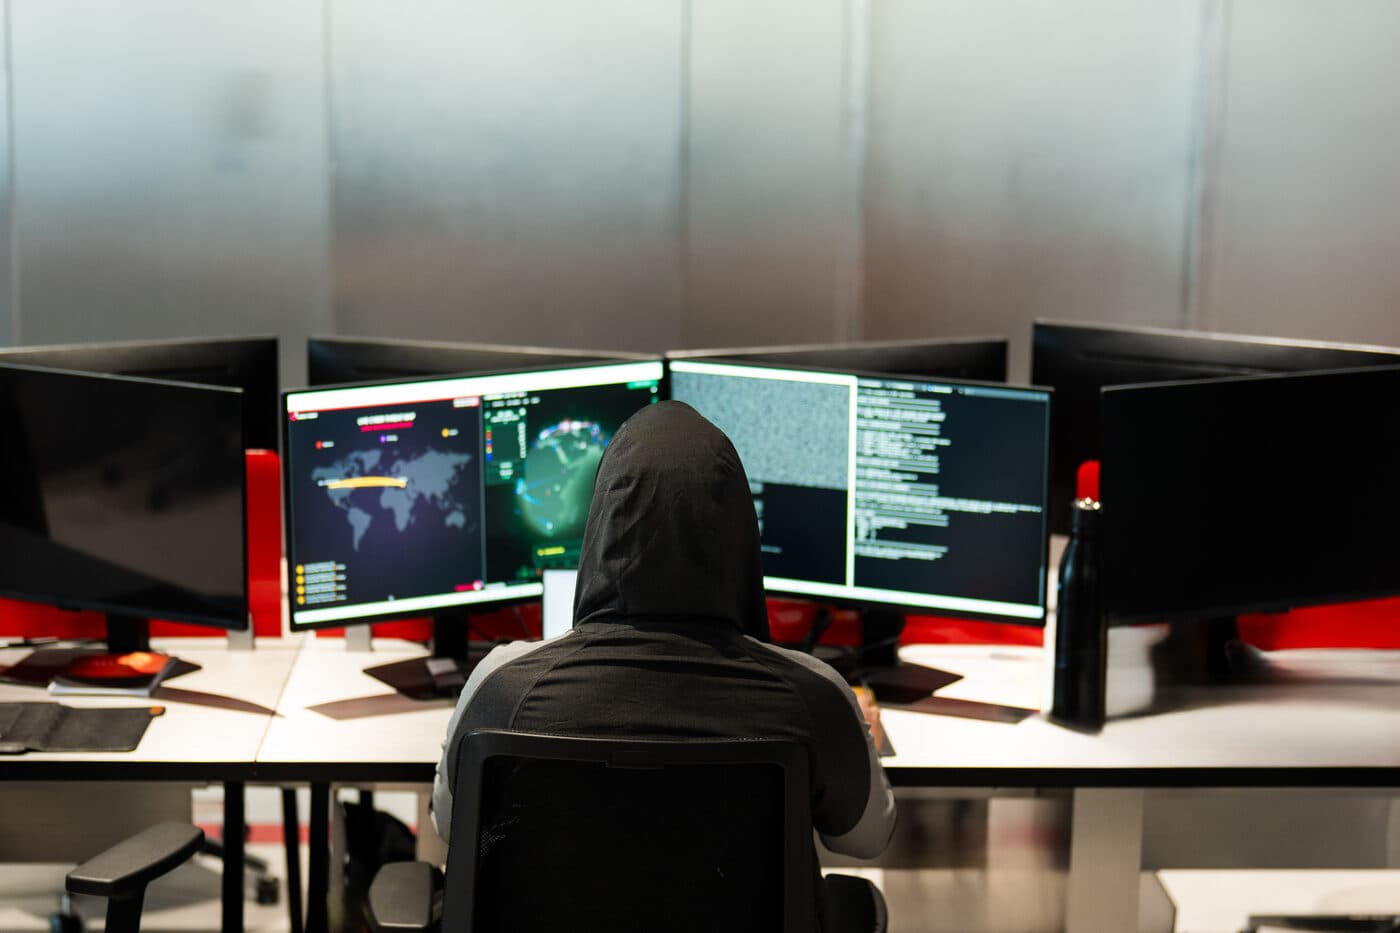
The adversary's side of the screen
01

Smarter cyber threats

Attackers now use AI-driven tactics, zero-day exploits, and social engineering to breach defenses faster than ever.

02

Expanding attack surface

Cloud systems, remote work, and connected devices have exploded the number of entry points.

03

Overloaded teams

IT and security teams struggle with alert fatigue, tool sprawl, and limited 24/7 visibility.

04

Compliance pressure

Meeting ISO 27001, GDPR, and PCI DSS requirements has become a constant challenge.

05

Longer dwell time

Threats often remain undetected for weeks — turning minor incidents into costly breaches.

Delivery models

One SOC. Three ways to run it.

The workflow, the platform, and the discipline are the same in every model — the only difference is who operates it. Most clients start with SOC as a Service; the deeper your own team, the more you can share the load.

Fully managed

Most chosen

SOC as a Service

We run it all, from our SOC.

A fully outsourced, cloud-delivered SOC on subscription — our watch floor, our full stack (SIEM, SOAR, EDR, threat intel, AI automation), our certified analysts. No infrastructure to buy, no team to hire.

Who runs it

Zentara runs everything, end to end.

Best for

Mid-scale organizations facing enterprise-grade threats without enterprise budgets or teams.

Talk to an expert

Shared / hybrid

Co-Managed SOC

We share the watch with your team.

A shared model that fits how your team already works — you cover business hours or L1/L2, we cover nights, weekends, and L3 depth. Any split works, with detection engineering and joint incident command layered on top.

Who runs it

You and Zentara operate together, by an agreed split.

Best for

Organizations and MSSPs with a capable day-shift team but gaps in after-hours or specialist depth.

Talk to an expert

Your SOC, our analysts

SOC Staff Augmentation

Our certified analysts, embedded in your SOC.

We place vetted, certified analysts (CEH, CIHE, Security+) into your security operation under your command structure — with Zentara L3 escalation behind them. Transparent manday rates, aligned to INKINDO standards.

Who runs it

You run the SOC and keep control; we supply the people.

Best for

Organizations that run their own SOC but can't hire the certified bench fast enough.

Talk to an expert

Need a SOC built and handed to you outright? That’s a different engagement — Turnkey SOC (Build-Operate-Transfer).

Packages

Coverage sized to your risk

Every package is the same 24/7 operation: L1, L2 and L3 analysts on Zentara's own platform. What changes is depth — what we watch, how often we hunt, and how much we handle for you.

COREThe 24/7 foundation

For organisations that need round-the-clock eyes on their critical systems, with full L1–L3 response behind every alert.

Includes

  • 24/7 monitoring with full L1, L2 and L3 support
  • SIEM detection on alert and attack logs
  • 5 custom detection use cases a year
  • Monthly report, presented to your team
  • An annual threat hunt and ZEN INTEL scan
Discuss CORE
Recommended

EDGEDetection in depth

For organisations under audit or regulator scrutiny that need network and host detection, regular hunting and tested defences.

Everything in CORE, plus

  • Network and host intrusion detection (NIDS and HIDS)
  • Vulnerability assessment twice a year
  • Threat hunting and ZEN INTEL scans twice a year
  • 10 custom use cases a year and a custom request every month
  • Multi-channel alerts and an annual awareness session
Discuss EDGE

APEXThe full operation

For high-stakes institutions that need every log analysed, monthly hunting and incident response on hand.

Everything in EDGE, plus

  • Full sensor suite: honeypot, network forensics, threat intelligence
  • Every log analysed, with a further month kept offline
  • Monthly threat hunting and continuous ZEN INTEL monitoring
  • Incident response assistance, three times a year
  • Quarterly vulnerability assessment and unlimited use cases
Discuss APEX

Built by Zentara

Our own platform, in every package

The tools behind the packages are ours. We build them, run them and answer for them.

  • SIEM

    ZX

    Collects, correlates and enriches your logs in real time. The detection layer of every package.

    See the product
  • Threat intelligence

    ZEN INTEL

    Checks your domain for leaked credentials, breach data and dark-web exposure. Continuous monitoring on APEX.

    See the product
  • Security appliance

    ZENTARA appliance

    Runs the package's sensors inside your environment. In the cloud, on an instance you provide.

Compare

Every inclusion, side by side

Download the full service deck
Every inclusion, side by side
Monitoring & detection
Security monitoring 24/7CORE: IncludedEDGE: IncludedAPEX: Included
SOC supportEvery alert can move from triage to investigation to response.CORE: Full: L1, L2, L3EDGE: Full: L1, L2, L3APEX: Full: L1, L2, L3
Log management & SIEMZXRuns on ZX, Zentara's own SIEM.CORE: IncludedEDGE: IncludedAPEX: Included
Detection technologiesSensors run on the ZENTARA security appliance in your environment.CORE: SIEM onlyEDGE: SIEM + NIDS & HIDSAPEX: Full: SIEM, NIDS, HIDS, honeypot, network forensic tools, threat intelligence
Logs integrated & analysedAll logs adds operational logs, such as performance and process events.CORE: Alert & attack logsEDGE: Alert & attack logsAPEX: All logs
Log retentionOnline logs are ready to analyse in real time. Offline logs are archived and extracted before analysis.CORE: 1 month onlineEDGE: 1 month onlineAPEX: 1 month online + 1 month offline
Platform & assets
Security applianceThe ZENTARA appliance, on premise. In the cloud, an instance or VM you provide.CORE: IncludedEDGE: IncludedAPEX: Included
Asset integrationOnboarding the assets defined in scope.CORE: OnceEDGE: Twice a yearAPEX: Continuous
Asset changesAdding new assets to monitoring during the contract.CORE: Not includedEDGE: Not includedAPEX: Unlimited
Custom use casesNew SIEM detection rules, built for your environment.CORE: 5 a yearEDGE: 10 a yearAPEX: Unlimited
Case management mobile appFor 5 users.CORE: IncludedEDGE: IncludedAPEX: Included
Hunting, response & intelligence
Threat huntingCORE: Once a yearEDGE: Twice a yearAPEX: Monthly
Incident responseHands-on assistance when a valid incident occurs.CORE: Not includedEDGE: Not includedAPEX: 3 times a year
ZEN INTEL threat intelligenceZentara-builtExtended threat intelligence for one domain.CORE: 1 scan a yearEDGE: 2 scans a yearAPEX: Continuous monitoring
Vulnerability assessmentScanning of the covered scope, with a report.CORE: Not includedEDGE: Twice a yearAPEX: Quarterly
Case notificationHow we reach you when we confirm a valid attack: email, WhatsApp, Telegram or your ticketing system.CORE: EmailEDGE: Multi-channelAPEX: Multi-channel
Reporting & advisory
SOC reportingEvery report is presented to your team. Monthly reports arrive by day 3 of each month.CORE: MonthlyEDGE: Monthly + annualAPEX: Monthly, half-year + annual
Custom requestsAd-hoc reports, or a search for a specific alert.CORE: 3 a yearEDGE: 1 a monthAPEX: 10 a month
Subject-matter expert supportTime with our specialists on security questions in your environment.CORE: 1 ticket a yearEDGE: 3 tickets a yearAPEX: Unlimited
Security advisoryAdvisories when a relevant threat emerges.CORE: As issuedEDGE: As issuedAPEX: As issued + playbook
Security awareness sessionCORE: Not includedEDGE: Once a yearAPEX: Twice a year
Compliance supportCORE: As neededEDGE: As neededAPEX: As needed
Maturity scorecardA security maturity assessment, repeated to show progress.CORE: At the startEDGE: Start and endAPEX: Start, half-year and end
Discuss EDGE

Packages are scoped to the assets you define. Scope and price are confirmed in writing after a scoping call.

Service levels

A clock on every severity

Every alert is classified on arrival. Each severity has its own response and containment target.

  1. P1 · Critical

    Active attack causing service outage or data loss

    Response
    15 minutes
    Containment
    2 hours

    We tell you by: Phone + email

  2. P2 · High

    Major incident: no data loss yet, but high risk

    Response
    30 minutes
    Containment
    4 hours

    We tell you by: Email + portal

  3. P3 · Medium

    Suspicious activity that needs investigation

    Response
    1 hour
    Containment
    8 hours

    We tell you by: Portal

  4. P4 · Low

    Informational or benign alerts

    Response
    4 hours
    Containment
    24 hours

    We tell you by: Monthly report

The problem

Building an internal SOC takes 18 months and Tier 2/3 analysts the market does not have. Meanwhile alerts pile up, dwell times grow, and regulators expect answers.

Track record

Operating dedicated and managed SOCs for national banks, telecom operators, and regional lenders.

Our approach

  • 24/7/365 monitoring, detection, and response run by certified analysts (GCIA, GCIH, OSCP, CEH).
  • Built on the ZX platform — full SIEM capability without the buildout, with behavioral analytics and AI-assisted triage.
  • Infrastructure stays client-hosted where data sovereignty demands it — built for hybrid environments.
  • Threat hunting included, not just alert monitoring.
  • Monthly reporting on executive and technical tracks.

Methodology

The incident response workflow

Five stages, run the same way at 3 PM and 3 AM — from readiness to verified recovery.

01

Preparation

Build readiness and resilience before an incident occurs — asset onboarding, log integration, playbook alignment.

02

Detection & Analysis

Identify and confirm security incidents quickly and accurately — continuous correlation, behavioral analytics, L1–L3 triage.

03

Containment

Prevent threats from escalating or spreading within the environment, with pre-approved actions inside SLA.

04

Eradication

Eliminate the threat and ensure it cannot reoccur — root-cause closure, not reimaging and hoping.

05

Recovery

Return to full business operations with confidence, with verified restoration and lessons folded back into detection.

People, process, and technology — one operational picture

Inside the operation

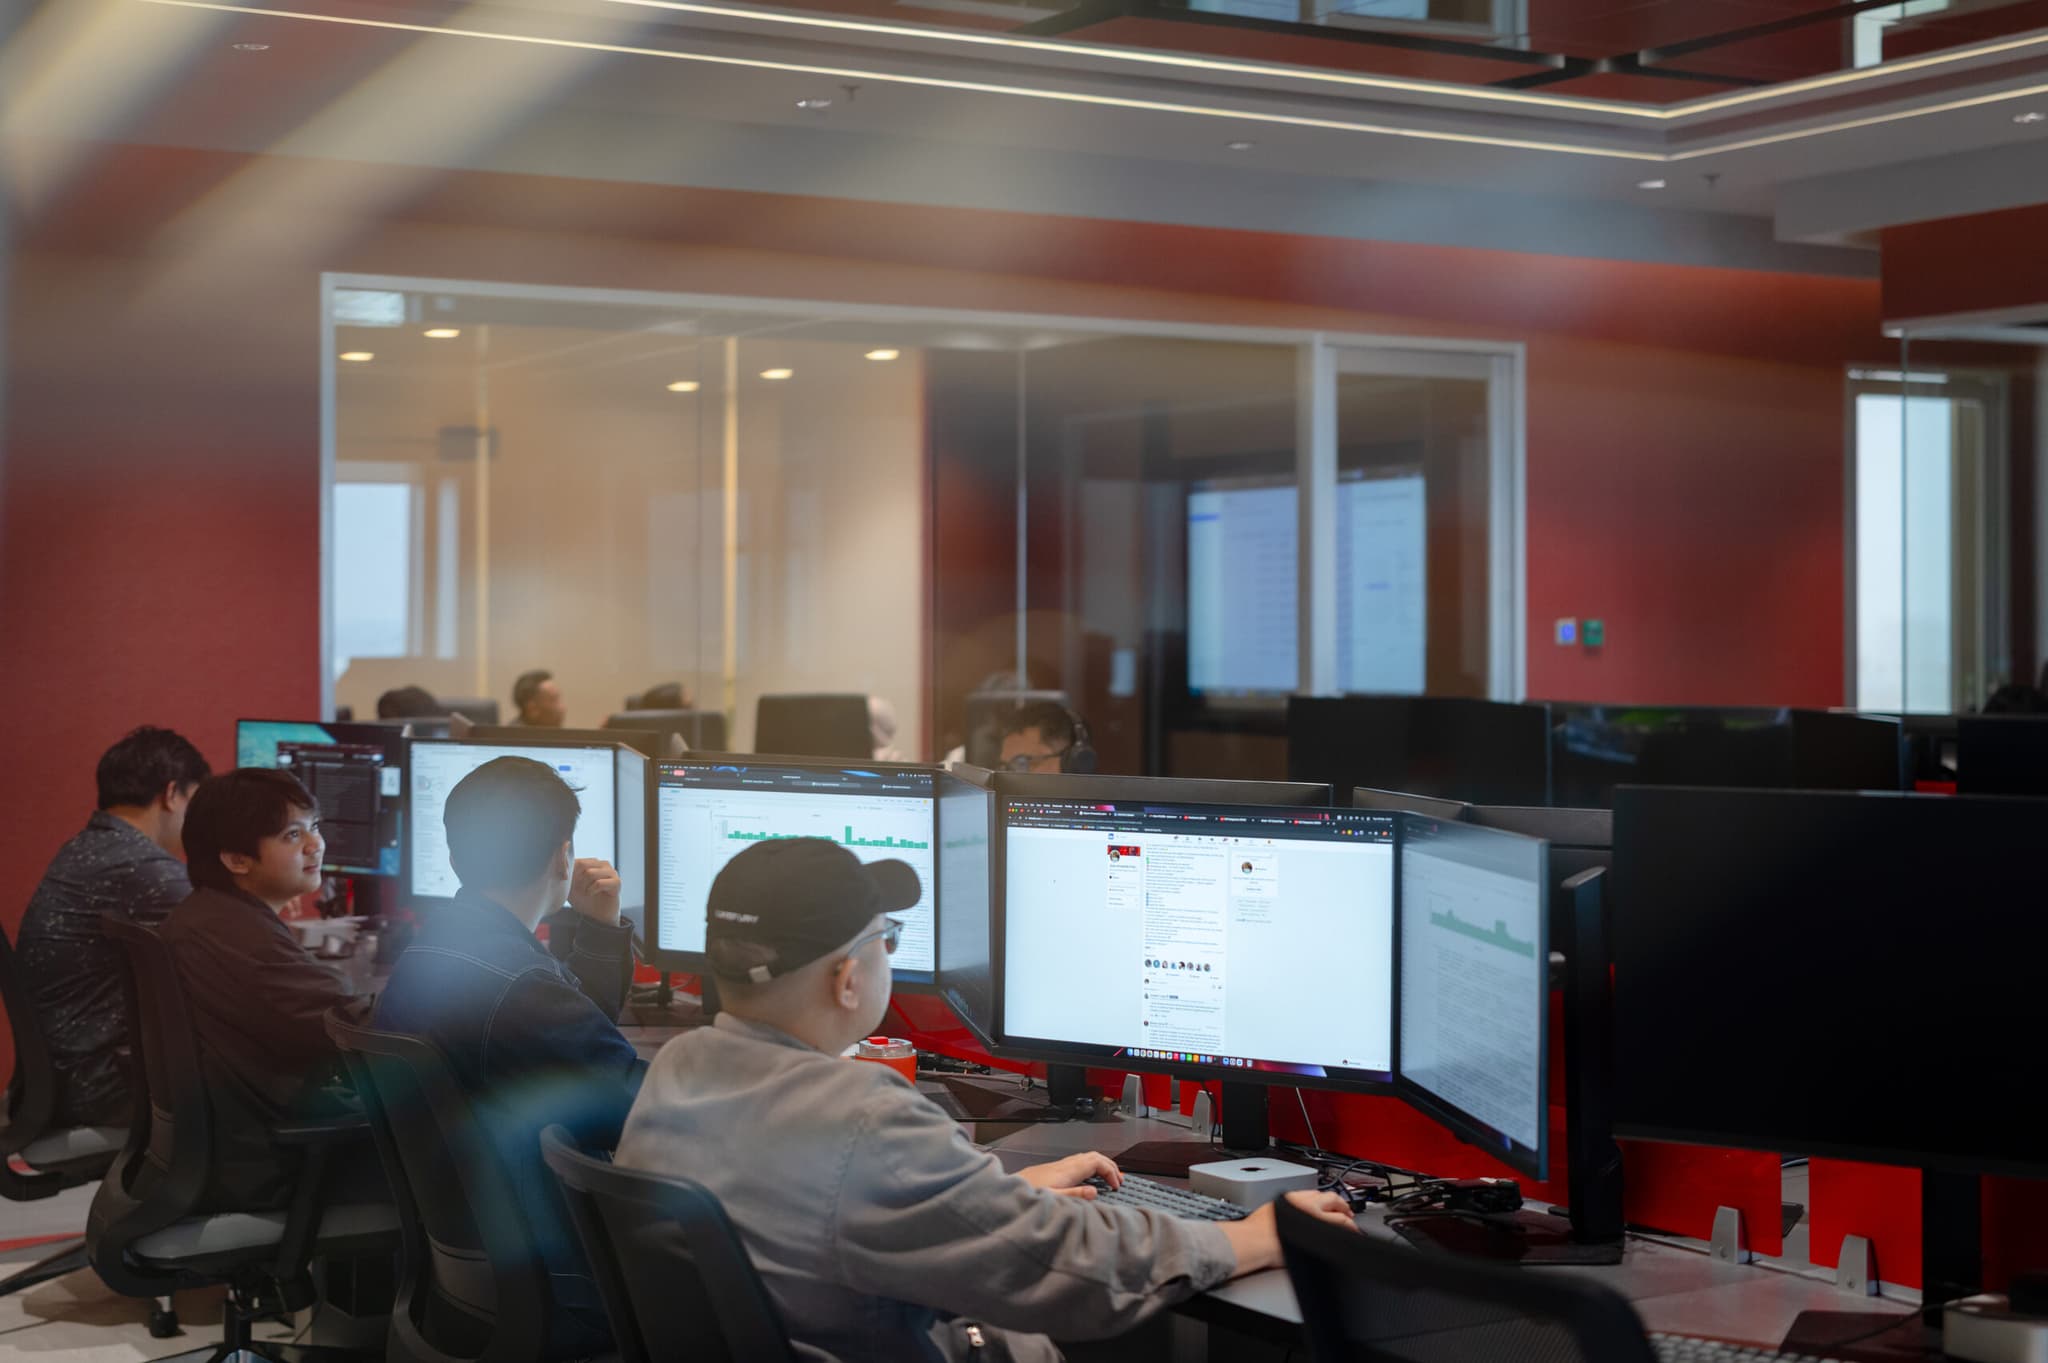
People, process, and technology — one operational picture

Certified L1–L3 analysts on the ZX platform, correlating telemetry across cloud and on-premise estates from Greater Jakarta. Your cybersecurity shouldn't sleep. That's why we don't either.

Hand off the watch

The fastest path to 24/7 coverage is our SOC, not your next hire

SOC as a Service puts our watch floor, platform, and certified analysts on your alerts from day one — no build, no bench to recruit. See it run against your environment.

Standards & frameworks

Every engagement is mapped to the regulations you answer to — so the evidence your auditors and regulators expect is a by-product of the operation, not a scramble.

ISO 27001:2022SOC 2 Type IIPCI DSSNIST CSFOJK / BI regulationMAS TRM

What you receive

  • 24/7 security monitoring & threat hunting
  • Real-time alerting & incident triage
  • Tiered SLA response — P1 acknowledged in 15 minutes, contained in 2 hours
  • Analyst reports & threat summaries

Go deeper

Technical documentation

For the engineers and architects in the room — the full methodology, in writing.

The deck our team walks new clients through: how the SOC is delivered, how it connects to your on-premise and cloud estate, the response targets by severity, and the three packages compared line by line.

  • The delivery models, and who runs what in each
  • Architecture and workflow, on premise and in the cloud
  • The incident response workflow, from preparation to recovery
  • Service levels by severity, from P1 to P4
  • ZX, Zentara's own SIEM, inside the operation
  • CORE, EDGE and APEX, compared line by line

A technical reference for security architects, SOC leads, and infrastructure engineers evaluating managed security operations. It details the detection engineering principles, platform architecture, deployment topology, and operational workflows underpinning Zentara's AI-Powered SOC.

  • SOC architecture: design principles, tradeoffs, and the core technology stack
  • Detection methodology — AI behavioral analytics vs. rule-based approaches
  • Deployment models compared: on-premise, cloud, and hybrid topologies
  • The incident response pipeline, step by step
  • Integration architecture for on-premise and cloud estates
  • SLA engineering, performance metrics, and competitive positioning

Zentara's playbook for building or upgrading an AI-augmented SOC that is operationally capable and regulation-aligned in the ASEAN and Indonesian context.

  • Where SOC operations are going in 2026 — ASEAN and Indonesia specifically
  • What AI actually does (and doesn't do) for SOC operations
  • A roadmap and maturity model to benchmark your SOC against
  • The checklist: is your SOC AI-ready and regulation-compliant (OJK, BSSN, ISO)?
  • A people-process-technology workflow you can tailor
  • The indicators and metrics that define SOC success

FAQ

Common questions

Straight answers. If yours isn't here, ask us directly.

They're three ways to run the same operation. SOC as a Service is fully managed on our stack — the fastest path to 24/7 coverage with no build or bench to hire. Co-Managed shares the watch with your team (you cover day or L1/L2, we cover nights or L3). Staff Augmentation embeds our certified analysts into your own SOC while you keep control. Same workflow, same SLAs — the only difference is who operates it.

Yes. Operations are vendor-agnostic — we run engagements on Elastic, Splunk, Sentinel, SentinelOne, Trellix, and the ZX platform, integrating with the tools you already own.

P1 incidents are acknowledged within 15 minutes and contained within 2 hours under the tiered SLA — with pre-approved containment actions executed inside SLA, not waiting on a call chain.

No. Infrastructure stays client-hosted where data sovereignty demands it — the operation is built for hybrid environments, with monitoring and response delivered over your estate.

Included, not optional. The engagement covers proactive threat hunting alongside 24/7 monitoring, detection, and response — because waiting for alerts means waiting out dwell time.

Monthly reporting on two tracks — executive and technical — plus real-time alerting, incident triage records, analyst reports, and threat summaries throughout the engagement.

Scope a Managed SOC engagement

Send us your context — we'll respond with scope, method, and timeline. No generic pitch decks.